Another full home router takeover
Vulnerability analysis and ROP chain exploitation of an unauthenticated remote code execution flaw in MIPS home routers, along with lessons learned using AI as an offensive research assistant.
Vulnerability analysis and ROP chain exploitation of an unauthenticated remote code execution flaw in MIPS home routers, along with lessons learned using AI as an offensive research assistant.
Why AI and agentic workflows do not make cybersecurity fundamentals obsolete, but rather raise the price of overlooking the obvious and fundamentally reshape vulnerability management.
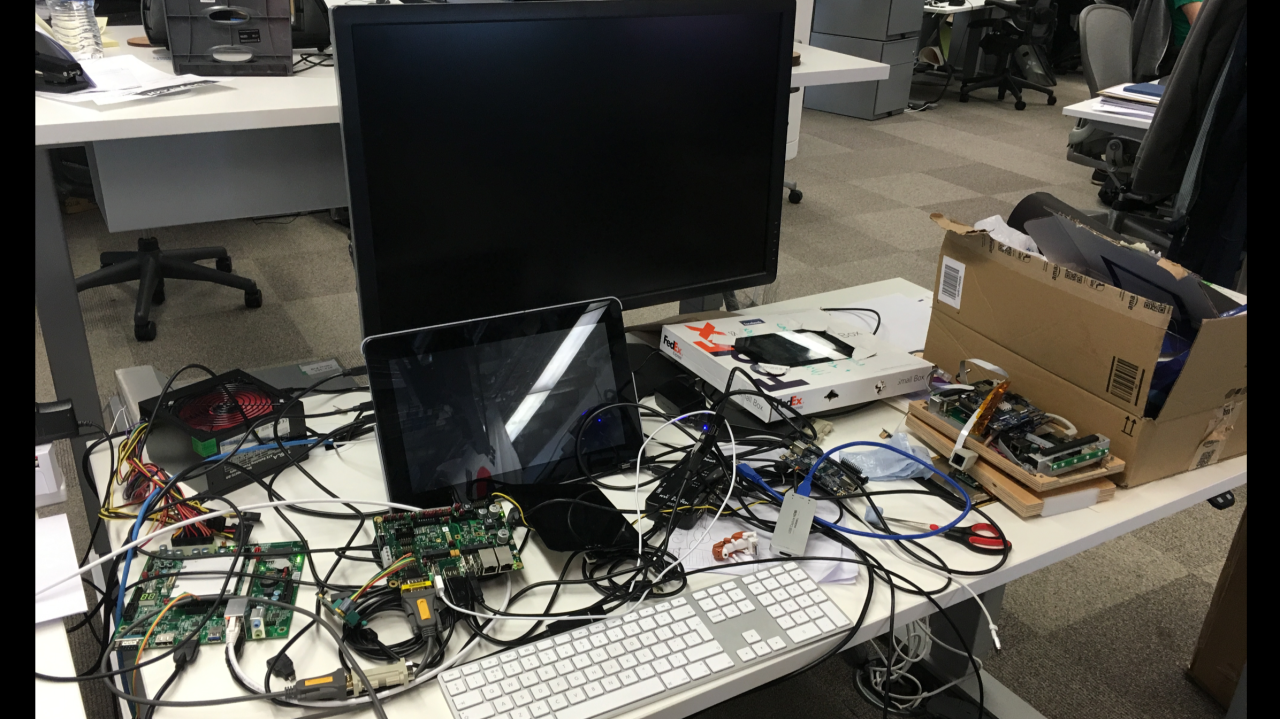
The engineering story of Gizmo at Facebook (Meta): how a cardboard prototype with MinnowBoard and TPM 2.0 evolved into a hardened, securely provisioned corporate device fleet.
Lessons learned from conducting an ethical hacking "exemption exam" CTF for university students at Sapienza University of Rome, exploring LLM usage in CTFs, anti-cheating, and hands-on offensive security.
Deep-dive into GLibC 2.23 heap exploitation: leveraging a single-byte overflow with House of Orange.
Exploring how text embeddings and Random Forest classifiers can predict CVSS vectors from CVE descriptions to alleviate NVD backlogs.
Vulnerability analysis of an unauthenticated remote code execution flaw in customer premises equipment (CPE) home routers.
Setting up fast, deduplicated, Git-based network backups across Mac and Linux systems using Bup and Docker.
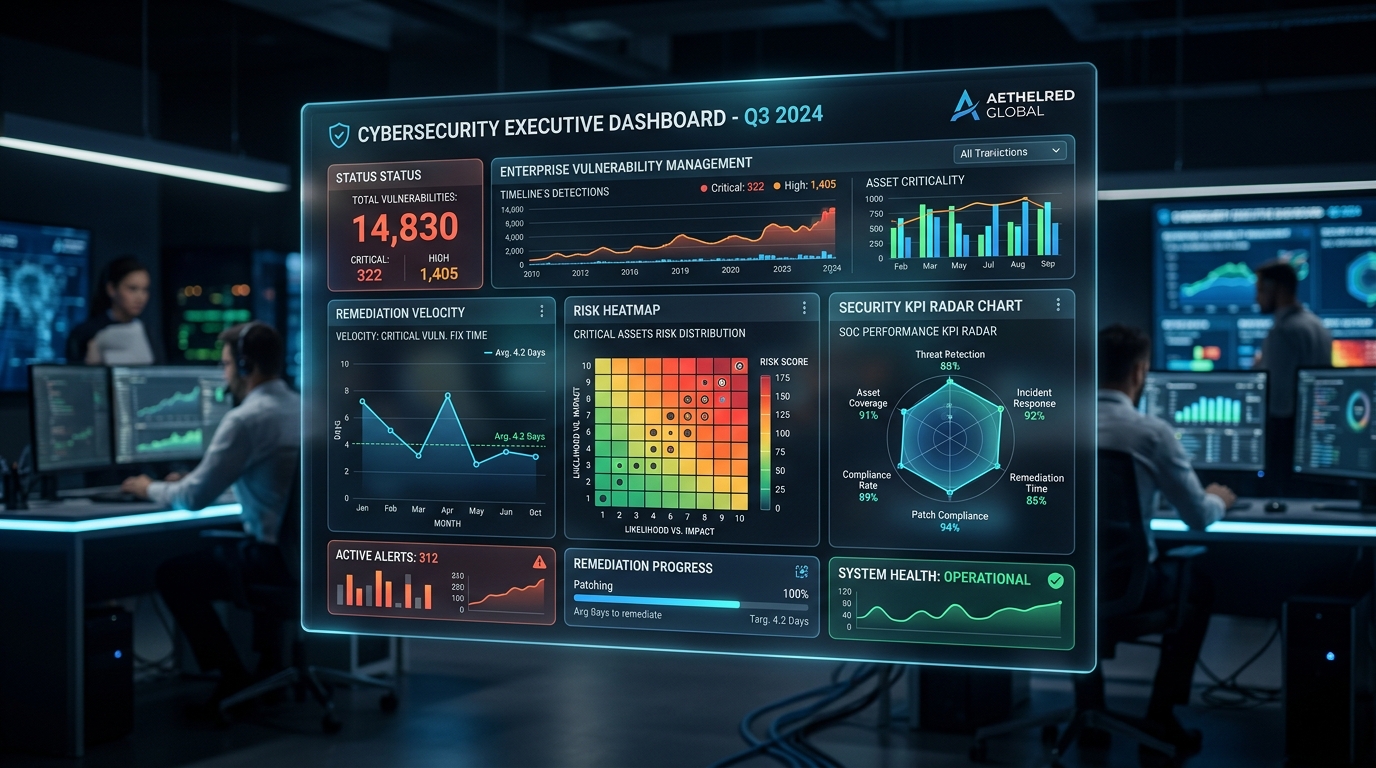
Practical framework and KPIs for measuring and scaling an enterprise vulnerability management program.
Reflections on recognizing, managing, and preventing stress and burnout in tech engineering and management.